Enterprise AI Security
Enterprise AI Security
Secure AI Adoption. Protect AI Applications, Agents and Data. Reduce AI Risk.
AI Security
Secure AI Adoption. Protect AI Applications. Reduce AI Risk.
Secure Enterprise AI Adoption
Help organizations adopt AI securely through governance, risk management, security architecture, policy, and controls across AI applications, agents, data, models, and integrations.
Secure Enterprise AI Usage
Protect employees and developers using ChatGPT, Microsoft Copilot, GitHub Copilot, Claude, Gemini, and other AI services. Reduce exposure of sensitive data, source code, credentials, and intellectual property while improving visibility into Shadow AI and enterprise AI usage.
Protect AI Applications and Agents
Secure internally developed and customer-facing AI applications, copilots and agents across architecture, development and runtime. Address prompt injection, sensitive-data exposure, excessive permissions, insecure integrations, agentic risks and other AI-specific attack paths.
AI Security Assessments
Improve AI asset discovery, Shadow AI visibility and AI security posture through governance, risk assessment, security policy and data-protection reviews. Identify security gaps, prioritize risk and develop practical remediation plans.
AI Red Teaming and Security Testing
Test AI applications and agents against realistic AI-specific attacks including prompt injection, indirect prompt injection, sensitive-data leakage, insecure integrations, excessive permissions, unsafe agent actions, security control bypass and unauthorized access to connected systems.
AI Security Architecture and Implementation
Design and implement secure AI environments, applications and agents through architecture review, AI application and agent security, data protection, integration security, access and permissions, governance controls and remediation planning.
Cybersecurity Meets AI Security
Cybersecurity Meets AI Security
AI does not replace traditional cybersecurity requirements — it expands them. Organizations must continue protecting identities, networks, cloud environments, applications and data while also securing AI usage, applications, agents, integrations and AI-driven workflows.
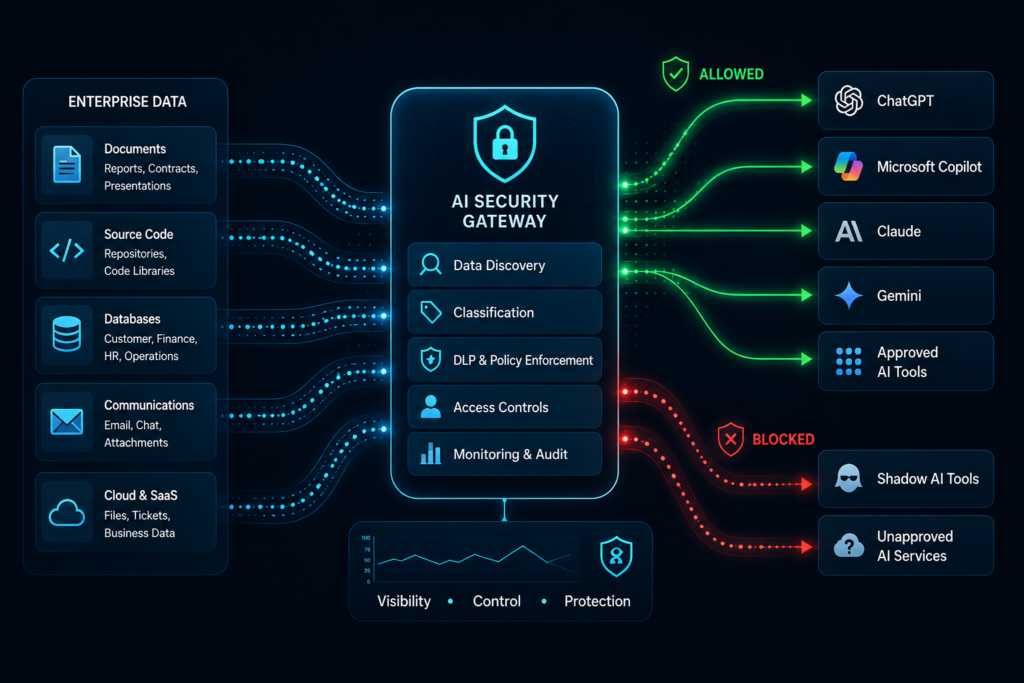
How can we allow employees to use AI without exposing corporate data?
Establish acceptable use standards, tenant controls, AI application and integration controls, data handling guardrails, Shadow AI visibility, and sensitive-data protection for employees and developers using enterprise AI assistants and copilots.
How do we secure the AI applications, copilots and agents we are developing?
Secure AI applications, copilots and agents through architecture review, API and integration security, permission design, runtime controls and testing for prompt injection, insecure integrations, excessive permissions and unsafe agent actions.
How do we govern and secure AI across our organization?
Improve AI asset discovery, Shadow AI visibility, governance, auditability, policy enforcement and data protection while prioritizing AI-related risk across business, security and technology teams.
From Assessment to Implementation
Assess → Architect → Evaluate → Integrate → Implement → Optimize
IFSEC goes beyond assessments. We help organizations design, evaluate, integrate and implement security controls across enterprise AI platforms, applications and agents — including AI security architecture, data protection, identity and access controls, application and API security, and security technology evaluation.
We bring these disciplines together by combining established enterprise cybersecurity expertise with emerging AI security capabilities.
FAQ
AI Security Questions
Get clear answers on secure AI adoption, AI applications and agents, governance, assessments and AI-specific security testing.